Trusted with financial data. By design.
Your customers' accounting, banking and payment data passes through us. That sets the bar. Isolated per customer, encrypted end to end, hosted in Europe, audited externally.
Powering the best software teams
Instant connectivity built to last
We have what it takes to operate reliably in the AI era.

EU data safety
Your data stays in Europe. Hosted in the EU and fully GDPR compliant. No transfers outside the union, no US cloud dependency for your legal team to work around, no residency clause to negotiate.

ISO 27001
Certified to the international standard for information security management. Controls, risk assessments and incident procedures, audited and re-verified externally.

Data layer & storage
You decide what gets stored. Live reads pass through and leave nothing behind. The data layer keeps a copy because that's its purpose, opt-in per connection, with you choosing which entities sync and how much history loads.

Encryption
Encrypted in transit and at rest. Credentials and tokens never sit in plain text, and never sit in your database.

Isolation
Multi-tenant by construction. Every record carries its consumer, connection and folder, so isolation is structural, not a query filter.

Penetration testing
Tested by an independent third party. Findings remediated and re-tested, report available under NDA.
Built to pass your security review
Where your customers' data sits, who holds the credentials, and who audits us. Answered before you ask.
Three models, one deliberate choice
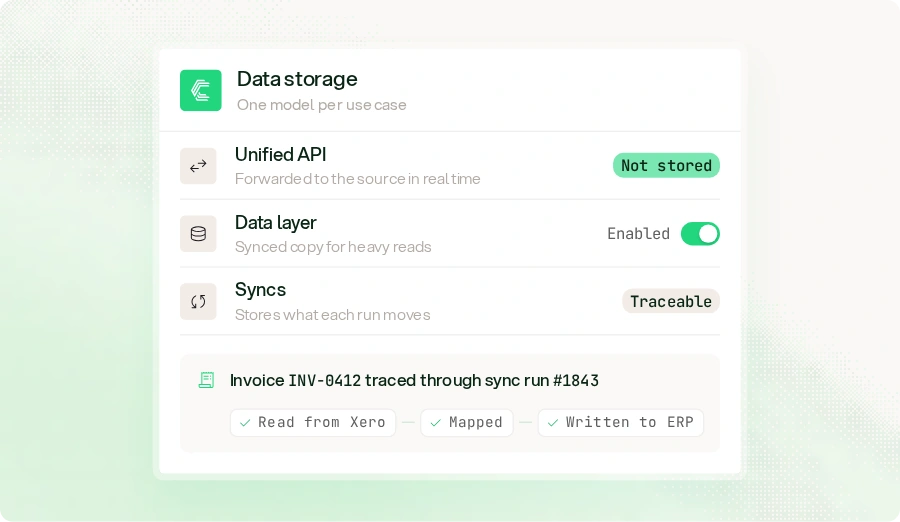
With the Unified API, every call is forwarded to the source system in real time, normalised and returned. The customer's data never sits inside Chift. The data layer is the opt-in exception: reads served from a copy we keep in sync, so heavy queries and long history return fast. Syncs store what they move, which is how you can trace a single invoice through a run. You pick the model per use case, and nothing changes without you enabling it.
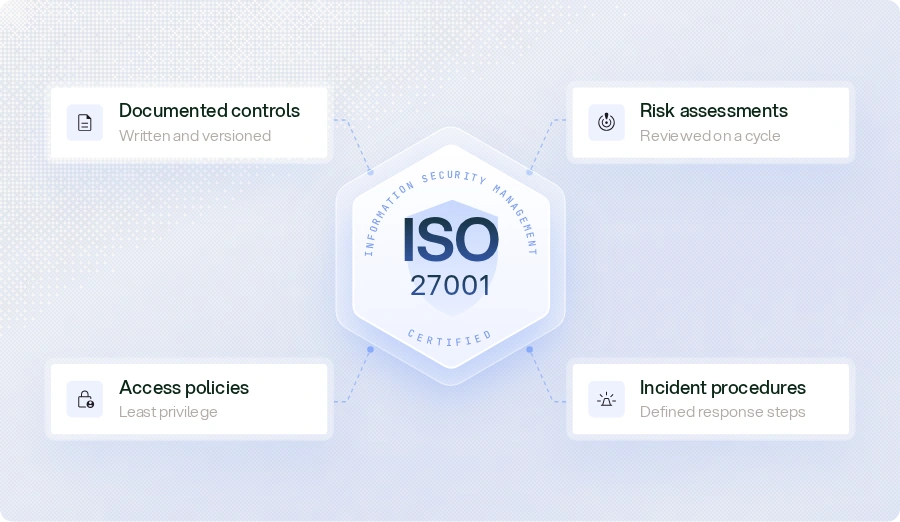
ISO 27001, and what that actually means
Being certified isn't a badge, it's a set of obligations. Documented controls, risk assessments, access policies and incident procedures, all audited by an external body and re-verified on a cycle. We follow the industry's highest standards of security and privacy, and an auditor checks that we still do. Certificate available for your vendor file.
You never hold a token
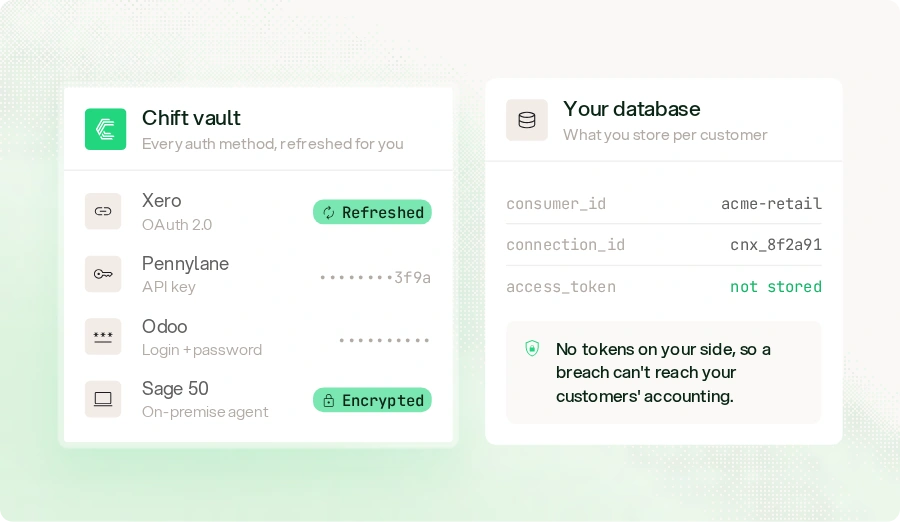
Every connector authenticates differently: OAuth, API keys, credentials, on-premise agents. We handle every method a source system offers, store the credentials securely, and refresh them before they expire. Nothing lands in your database, so a breach on your side can't expose your customers' accounting software. On-premise agents keep their sensitive fields encrypted on the machine and masked on screen.
You build the product, we handle the connectivity
One integration to every financial tool in Europe, ready for your product and your agents.